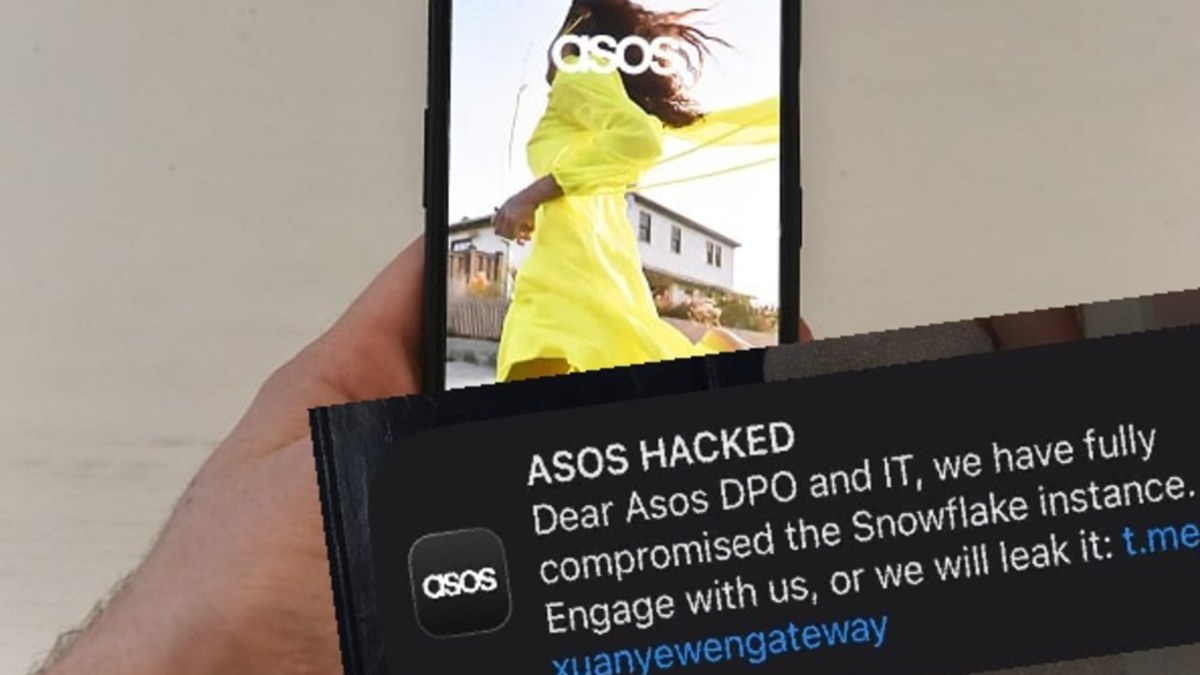
ASOS customers opening their phones on Tuesday night were met with an alarming, direct message from the global fast-fashion giant. Instead of a typical discount offer or shipping update, the official ASOS app delivered a blunt ransom note.
The notification claimed that the company's systems had been compromised and threatened to leak sensitive customer data. Here is what we know about the developing situation.
What Happened?
The security alert, sent around 8 p.m. AEST, read:
"ASOS hacked. Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it."
The push notification embedded a link directing users to a newly created channel on the messaging app Telegram, labeled "Xuanye group gateway." Cybersecurity firm Sophos noted that its specialists had not previously encountered this specific group on monitored channels.
ASOS, which is valued at approximately £602 million ($1.15 billion) and boasts 16.4 million active customers worldwide, is currently investigating whether a confirmed data breach has occurred.
Why This Attack Is Highly Unusual
Cybersecurity experts say the method of the attack is incredibly bold. Rather than quietly stealing data in the background, the threat actors used the retailer’s own infrastructure to broadcast their demands.
"The hackers appear to have done something particularly brazen: turned ASOS’s own app into their ransom note," said Charlotte Wilson, head of enterprise at cybersecurity firm Check Point.
Experts point out that this indicates a deeper level of infiltration:
- Multiple Doors Opened: Sending a push notification requires access to the app's notification system.
- Database Threat: The message specifically names "Snowflake," a cloud data storage platform used by many major corporations. Snowflake has previously been linked to high-profile breaches at Ticketmaster, Santander Bank, and AT&T.
- Broad Access: If both claims are true, hackers likely obtained credentials that unlocked multiple secure systems.
The Immediate Fallout and Next Steps
The financial markets reacted swiftly to the security scare. ASOS’s share price, which had been on an upward trend, plunged by nearly 12% on the London Stock Exchange as news of the suspected compromise spread.
While the ASOS website remains fully operational, security experts are urging the public to be on high alert. High-profile cyber incidents usually trigger a wave of secondary phishing scams.
Cybercriminals frequently exploit the confusion by sending fake emails or text messages pretending to be from the affected brand. Shoppers should avoid clicking on links asking them to reset passwords, verify payment details, or claim order refunds until ASOS releases an official statement.